
Cross-framework compliance mapping is the practice of aligning a single set of security controls to the requirements of multiple regulatory standards simultaneously. By implementing a control once and mapping it to several frameworks, organizations eliminate the redundant work of building separate programs for each audit. This approach directly reduces the labor hours required for evidence collection and policy drafting, which is the primary driver of compliance costs for growing teams.
The Hidden Cost of Siloed Compliance
Most organizations treat each compliance framework as a distinct project. A team preparing for SOC 2 builds a set of controls, collects evidence, and writes policies. When the same team later prepares for ISO 27001, they often repeat the process from scratch. This siloed approach creates a significant operational drag. The evidence collected for one audit is rarely formatted or structured in a way that satisfies the requirements of another. Consequently, staff spend weeks re-gathering the same screenshots, re-writing similar policies, and re-configuring the same technical safeguards.
The financial implication is direct. Compliance is a labor-intensive function. If a team spends 200 hours preparing for SOC 2 and another 150 hours for ISO 27001, the total cost is the sum of both. However, if 60% of the work is identical, the team is paying for the same labor twice. This redundancy is the primary reason compliance budgets balloon as the number of frameworks increases. It is not the software that is expensive; it is the duplicated human effort required to feed separate systems with the same data.
How Mapping Eliminates Redundancy
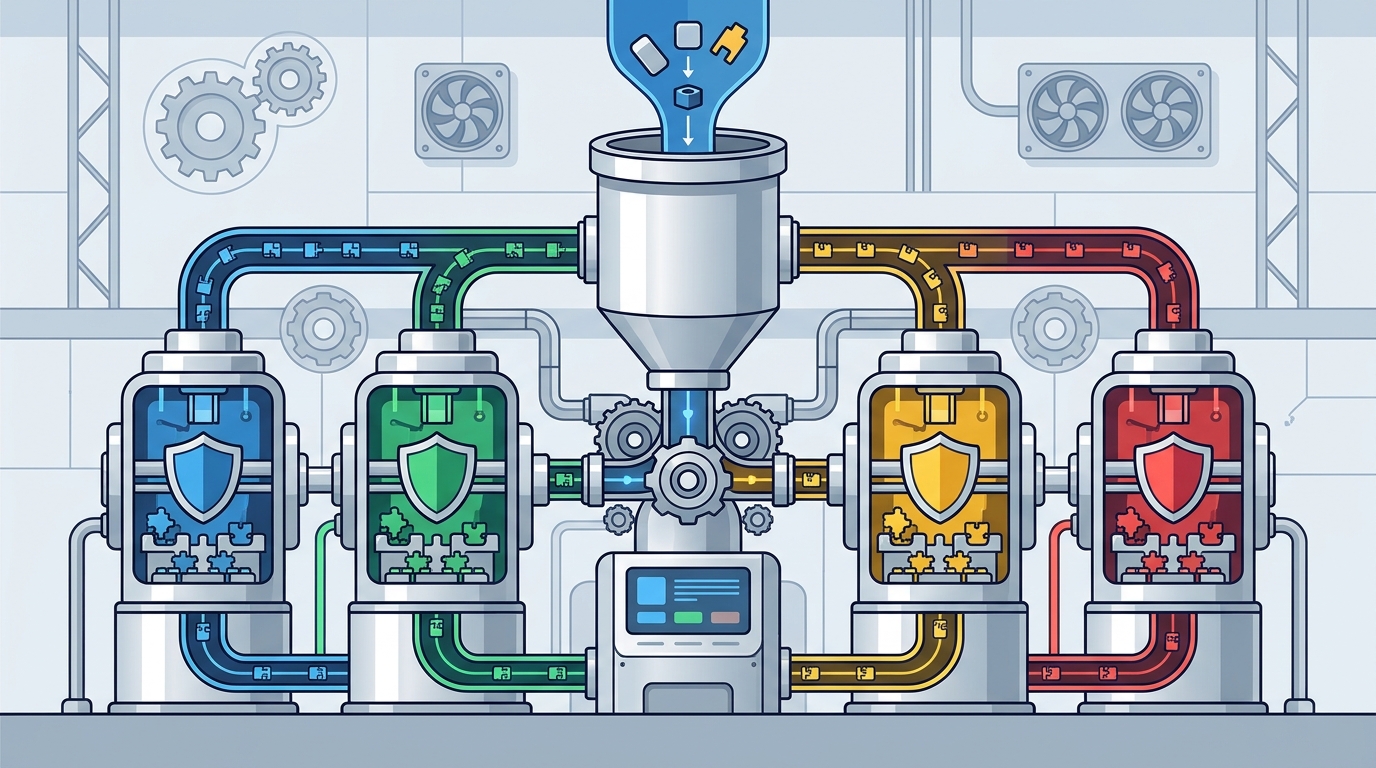
Cross-framework mapping inverts this model. Instead of starting with a framework, the organization starts with a control. A control is a specific action or configuration, such as enforcing multi-factor authentication or conducting quarterly access reviews. In a crosswalked system, this single control is mapped to the specific clauses in SOC 2, ISO 27001, and NIST CSF that it satisfies. When the team implements the control and collects the evidence, that single artifact counts toward all three standards.
This is the core mechanism of time savings. The work is done once. The evidence is attached once. The policy is written once. The system then projects that single piece of work across every applicable framework. For example, a documented access control policy satisfies a requirement in SOC 2, a requirement in ISO 27001, and a requirement in NIST CSF. By treating the control as the unit of work rather than the framework, the team avoids the administrative overhead of managing three separate checklists. This structural shift is what allows a small team to manage a complex compliance portfolio without hiring a dedicated compliance department.
Quantifying the Time Savings
The savings from cross-framework mapping are not theoretical; they are measurable in hours and dollars. Consider a mid-sized SaaS company preparing for SOC 2 and ISO 27001. Without mapping, the team might spend 40 hours writing policies for SOC 2 and another 35 hours writing policies for ISO 27001. With a crosswalked library, the team writes the policy once, and the system maps it to both standards. The time saved is the difference between the sum of the individual efforts and the single unified effort. In many cases, this reduces the policy drafting phase by 40% to 60%.
The same logic applies to evidence collection. If a team must provide proof of vulnerability scanning for three different frameworks, they do not run the scan three times. They run it once, export the report once, and attach it to the control. The control then satisfies the requirements in all three frameworks. This eliminates the need to re-key data, re-format reports, or re-upload files for each audit. The result is a compliance program that scales linearly with the number of frameworks, rather than exponentially. Adding a new framework becomes a matter of mapping existing controls, not rebuilding the entire program.
The Role of Automation in Mapping
Manual cross-framework mapping is possible but fragile. Maintaining a spreadsheet that maps 50 controls to 10 frameworks is a full-time job in itself. The mapping breaks when a framework updates its requirements or when a control is modified. Automation is what makes cross-framework mapping sustainable. A modern GRC platform maintains the crosswalk as a living data structure. When a new framework is added, the system identifies which existing controls already satisfy its requirements. When a control is updated, the system flags which frameworks are affected.
This automation removes the cognitive load from the compliance team. They do not need to know the clause numbers for every framework. They only need to know if the control is implemented and if the evidence is current. The system handles the mapping. This is a critical distinction. Without automation, mapping is a one-time project that decays over time. With automation, mapping is a continuous process that keeps the program audit-ready. The time saved is not just in the initial setup; it is in the ongoing maintenance of the program.
Strategic Implications for Budgets
The financial impact of cross-framework mapping extends beyond labor hours. It affects the total cost of ownership of the compliance program. When a team can manage multiple frameworks with a single set of controls, they can negotiate better pricing with their GRC vendor. Vendors that support cross-framework mapping often price based on the number of frameworks, not the number of controls. This means that adding a new framework has a marginal cost, not a proportional cost. The team pays for the framework license, but they do not pay for the duplicated labor.
This model also improves the return on investment of the compliance program. The evidence collected is not just for the auditor; it is for the business. A well-mapped control library provides a clear view of the organization's security posture. It shows which risks are mitigated and which are not. This visibility allows the team to make informed decisions about where to invest in security. The compliance program becomes a strategic asset, not just a regulatory obligation. The time saved is reinvested in improving the security posture, which reduces the risk of a breach and the associated costs.
Key Takeaways
- Cross-framework mapping allows a single control to satisfy requirements across multiple standards, eliminating redundant work.
- The primary cost of compliance is labor, not software. Mapping reduces the labor required for evidence collection and policy drafting.
- Manual mapping is fragile and requires constant maintenance. Automated mapping keeps the program audit-ready with minimal effort.
- Adding a new framework to a crosswalked system has a marginal cost, not a proportional cost, improving the total cost of ownership.
- A well-mapped control library provides strategic visibility into the organization's security posture, turning compliance into a business asset.
Frequently Asked Questions
What is cross-framework compliance mapping?
Cross-framework compliance mapping is the process of aligning a single set of security controls to the requirements of multiple regulatory standards, such as SOC 2, ISO 27001, and NIST CSF, so that one piece of evidence satisfies all of them.
How much time does cross-framework mapping save?
Time savings vary by organization, but teams often report a 40% to 60% reduction in the time required for policy drafting and evidence collection when using a crosswalked system compared to managing frameworks in silos.
Is cross-framework mapping only for large enterprises?
No. Cross-framework mapping is particularly beneficial for small and mid-sized businesses that do not have a dedicated compliance team. It allows a small team to manage a complex compliance portfolio without hiring additional staff.
Can I do cross-framework mapping manually?
Yes, but it is difficult to maintain. Manual mapping using spreadsheets is fragile and breaks when frameworks or controls change. Automated mapping in a GRC platform is more sustainable and keeps the program audit-ready.
Does cross-framework mapping reduce the number of controls I need?
Not necessarily. The number of controls may remain the same, but the effort required to implement and evidence them is reduced. The same control satisfies multiple frameworks, so the work is done once.
Conclusion
Cross-framework compliance mapping is a fundamental shift in how organizations approach regulatory requirements. By treating the control as the unit of work, teams eliminate the redundant labor that drives up compliance costs. This approach allows a small team to manage a complex portfolio of frameworks, from SOC 2 to ISO 27001 to NIST CSF, without hiring a dedicated compliance department. The time saved is reinvested in improving the security posture, which reduces risk and strengthens the business. For growing organizations, this is not just a cost-saving measure; it is a strategic enabler that allows them to scale their security program in line with their business growth. Explore how Keel implements crosswalk-native GRC to see how this model works in practice.