What to Look for in a GRC Platform for Third-Party Compliance Risk
Look for a GRC platform that tracks vendors by criticality, automates review cadences, and links third-party risk directly to your internal controls. This approach ensures that a vendor's failure triggers a specific, documented response within your broader compliance program. KeelGRC provides this structure through a unified risk register and vendor inventory.
Vendor Inventory and Criticality Scoring
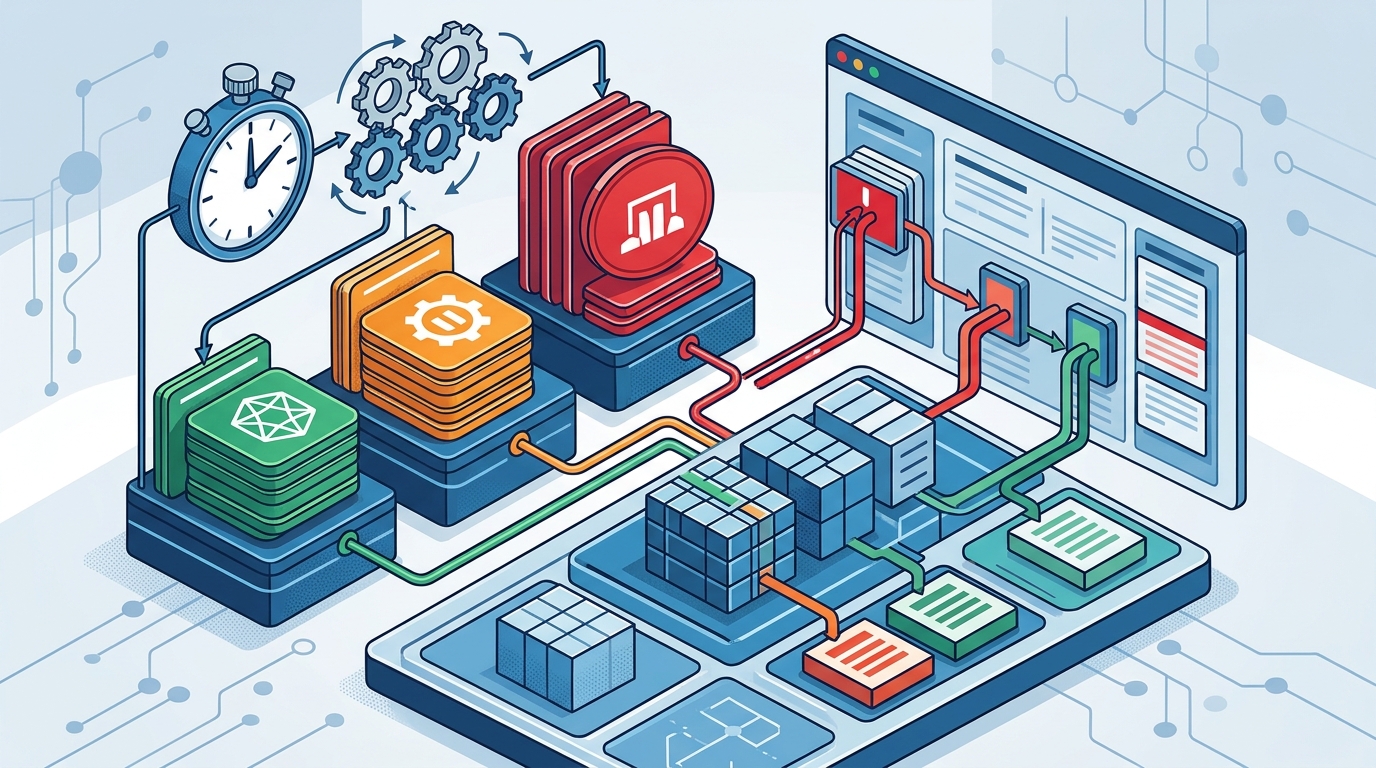
A robust vendor risk module begins with a complete inventory of every third party that touches your data or operations. You must classify these vendors by criticality to prioritize your limited security resources. High-criticality vendors, such as cloud providers or payment processors, require deeper scrutiny than low-risk software tools. This tiering ensures your team spends time where the potential impact is highest.
KeelGRC allows you to rate vendors based on the data they access and their role in your business. This classification drives the depth of the security questionnaire you send. By defining criticality upfront, you avoid the common mistake of treating every vendor with the same level of effort. This efficiency is critical for small teams managing a growing list of suppliers. according to Role Based Access
Automated Review Cadences and Evidence
Third-party risk is not a one-time check; it is an ongoing obligation. Your platform should support automated review cadences that prompt your team to re-evaluate vendors at set intervals. For example, a high-risk vendor might require an annual deep-dive, while a low-risk vendor only needs a simple confirmation every two years. This automation prevents reviews from slipping through the cracks during busy periods.
Efficiency comes from linking vendor evidence to your internal controls. When a vendor provides a SOC 2 report or a security questionnaire response, that document should serve as evidence for your own control requirements. KeelGRC connects vendor artifacts to the specific controls they satisfy, reducing duplicate work. This linkage means you are not just collecting PDFs; you are building a defensible audit trail that shows how you manage external dependencies.
Integration with the Internal Risk Register
Third-party risk does not exist in a vacuum; it is a subset of your overall organizational risk. A standalone vendor tool that does not talk to your main risk register creates a blind spot. You need a platform where a vendor's failure or a new vendor's onboarding automatically updates your internal risk register. This integration ensures that your risk owners see the full picture of exposure, including external factors.
In KeelGRC, the risk register scores each risk on likelihood and impact, and these risks link directly to the controls that treat them. When a vendor is flagged as high-risk, the associated internal risks are updated accordingly. This connection allows your leadership to see how third-party dependencies affect your overall compliance posture. It transforms vendor management from a siloed task into a core part of your governance strategy.
Policy Alignment and Contractual Expectations
Efficient vendor management requires clear policies that define your security expectations for third parties. Your GRC platform should help you draft, approve, and distribute these policies to vendors. A vendor risk policy outlines how you assess suppliers before granting access and what security standards they must meet. Without this documentation, your security team is negotiating from a position of weakness.
KeelGRC includes a library of framework-mapped policy templates, including a specific Vendor & Third-Party Risk Policy. You can customize these templates to match your operational reality and export them as branded PDFs. This ensures that your contractual agreements align with your internal compliance requirements. By standardizing your expectations, you streamline the onboarding process and reduce the friction of security negotiations.
Key Takeaways
- Classify vendors by criticality to prioritize security reviews and resource allocation.
- Automate review cadences to ensure ongoing compliance without manual tracking.
- Link vendor evidence directly to internal controls to avoid duplicate work.
- Integrate vendor risk with your main risk register for a complete exposure view.
- Use standardized policy templates to set clear security expectations in contracts.
- Choose a platform that supports cross-framework mapping for efficient evidence reuse.
Frequently Asked Questions
How often should we review high-risk vendors?
High-risk vendors that handle sensitive data or critical operations should be reviewed at least annually. This frequency ensures that any changes in their security posture are caught promptly. Lower-risk vendors can be reviewed on a longer cycle, such as every two or three years.
Can we use a vendor's SOC 2 report as our own evidence?
Yes, a vendor's SOC 2 report can serve as evidence for your vendor risk controls. However, you must verify that the report covers the specific services you use and that it is current. KeelGRC allows you to attach these reports directly to the relevant controls in your program.
What is the difference between vendor risk and third-party risk?
Vendor risk typically refers to the risks associated with suppliers you contract with, while third-party risk is a broader term that can include any external entity that impacts your operations. In practice, most GRC platforms use these terms interchangeably to manage external dependencies.
Do we need a separate tool for vendor risk management?
No, a separate tool often creates data silos and increases administrative burden. An integrated GRC platform like KeelGRC allows you to manage vendor risk within the same system as your internal controls and policies. This integration ensures that vendor data flows directly into your compliance reports.
How do we handle vendors that refuse to complete security questionnaires?
What frameworks apply to vendor risk management?
Several frameworks include requirements for vendor risk, including ISO 27001, SOC 2, and NIST CSF. KeelGRC crosswalks these requirements so that a single control can satisfy multiple frameworks. This approach reduces the effort required to demonstrate compliance across different standards.