7 Key Features to Look for in an MSP Compliance Automation Tool
Managed service providers (MSPs) face unique challenges when managing compliance for multiple clients. A standard single-tenant GRC tool often fails to scale for a book of business. The right MSP compliance automation tool must handle multi-tenancy, white-labeling, and per-client pricing. It should also automate evidence collection to reduce the manual workload for your team. This listicle outlines the seven critical features that separate a true MSP-focused platform from a generic enterprise tool. For additional details, review the Support Keel.
1. Multi-Client Console and Isolation
Manage every client workspace from a single, secure dashboard. An MSP needs a unified view of all client engagements without logging into separate accounts for each one. The platform must provide a console that rolls up coverage, open risks, and task statuses across your entire book of business. Crucially, each client must exist in an isolated workspace to ensure data separation and security.
2. White-Label Trust Centers and Reports
Deliver audit-ready proof under your own brand name. Clients expect deliverables that look like they came from your firm, not a third-party software vendor. A robust MSP tool allows you to white-label trust centers and readiness reports so they carry your logo and domain. This builds client trust and reinforces your position as the primary authority on their compliance posture.
3. Per-Client Partner Pricing
Scale costs with your book of business, not enterprise seats. Enterprise GRC tools often price based on internal user seats, which is inefficient for MSPs managing many clients with few internal staff. Look for a pricing model that charges per client workspace. This ensures your software costs align with your revenue and scale predictably as you add new clients.
4. Crosswalk-Native Control Libraries
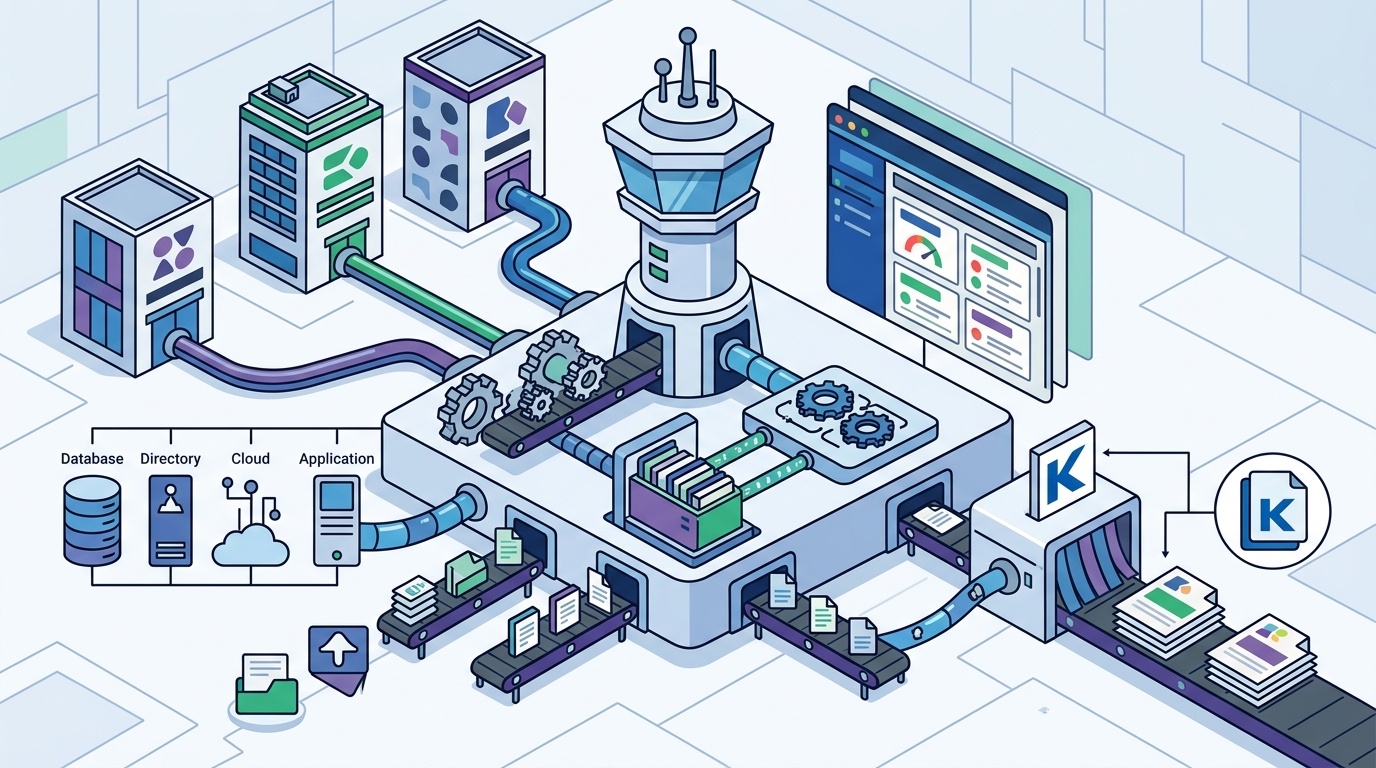
Reuse controls across frameworks to eliminate duplicate work. Many clients require multiple certifications, such as SOC 2 and ISO 27001. A crosswalk-native tool maps a single control to multiple framework requirements, so you collect evidence once and satisfy several standards. This architecture prevents the