Automated evidence collection streamlines SOC 2 readiness by continuously gathering proof that security controls operate as designed, eliminating the manual burden of screenshots and spreadsheets. For growing teams, this approach transforms compliance from a stressful, periodic scramble into a continuous, low-effort background process. KeelGRC enables this by integrating directly with your cloud and identity providers to pull live data into your compliance workspace.
The Hidden Cost of Manual Evidence
Manual evidence collection is the primary bottleneck for startups preparing for their first SOC 2 audit. Teams typically spend dozens of hours gathering screenshots of firewall rules, access logs, and policy documents just to prove a single control. This process is not only time-consuming but also fragile, as static screenshots quickly become outdated the moment a configuration changes. The result is a compliance program that consumes valuable engineering and security time that should be spent on product development.
Consider a typical SaaS company with 50 employees. Without automation, the security lead might spend two full days every month just updating evidence for a SOC 2 Type II report. This manual effort scales poorly as the company grows, creating a compliance debt that becomes increasingly difficult to manage. The implication is clear: manual processes do not scale with business growth, making automation a necessity rather than a luxury for growing teams.
How Continuous Monitoring Works
Continuous monitoring is the practice of automatically collecting and verifying evidence on a regular schedule, such as daily or weekly, rather than at a single point in time. In the context of SOC 2, this means your platform connects to your cloud infrastructure, identity provider, and code repositories to pull live data. For example, KeelGRC can run security checks against your Microsoft 365 tenant or cloud environment, filing the results directly as evidence against the relevant controls.
This approach ensures that your evidence is always current and reflects the actual state of your systems. When a control is tested, the auditor sees a trail of automated checks over the entire audit period, not just a single snapshot. This level of granularity provides a much stronger assurance of control effectiveness. The implication for growing teams is that continuous monitoring reduces the risk of audit failures due to outdated or inconsistent evidence, making the audit process smoother and more predictable.
Collect Once, Comply Everywhere
One of the most significant advantages of automated evidence collection is its ability to support multiple compliance frameworks simultaneously. KeelGRC is built on a crosswalk-native architecture, meaning that a single piece of evidence can satisfy requirements across multiple standards. For instance, evidence collected for a multi-factor authentication control can count toward SOC 2, ISO 27001, and PCI DSS at the same time.
This "collect once, comply everywhere" model drastically reduces the total volume of evidence you need to manage. Instead of maintaining separate evidence sets for each framework, you maintain one unified control and evidence graph. The implication is that as your company takes on new compliance requirements, the marginal cost of adding a new framework is significantly lower. This is particularly valuable for growing teams that may need to satisfy multiple customer or regulatory requirements without hiring a dedicated compliance team.
Preparing for the Audit
Automated evidence collection does not just save time during the preparation phase; it also makes the actual audit process faster and less disruptive. When auditors have access to a live, continuously updated evidence base, they can verify controls more efficiently. KeelGRC provides a dedicated auditor seat that allows auditors to view evidence and test work directly within the platform, without needing to request files or access your systems manually.
This transparency and ease of access can significantly reduce the duration of fieldwork. Auditors spend less time chasing down evidence and more time focusing on high-value judgment calls. The implication is a shorter, less stressful audit experience for your team. For growing companies, this means less disruption to daily operations and a faster path to obtaining the SOC 2 report that enterprise customers often require.
Getting Started with Automation
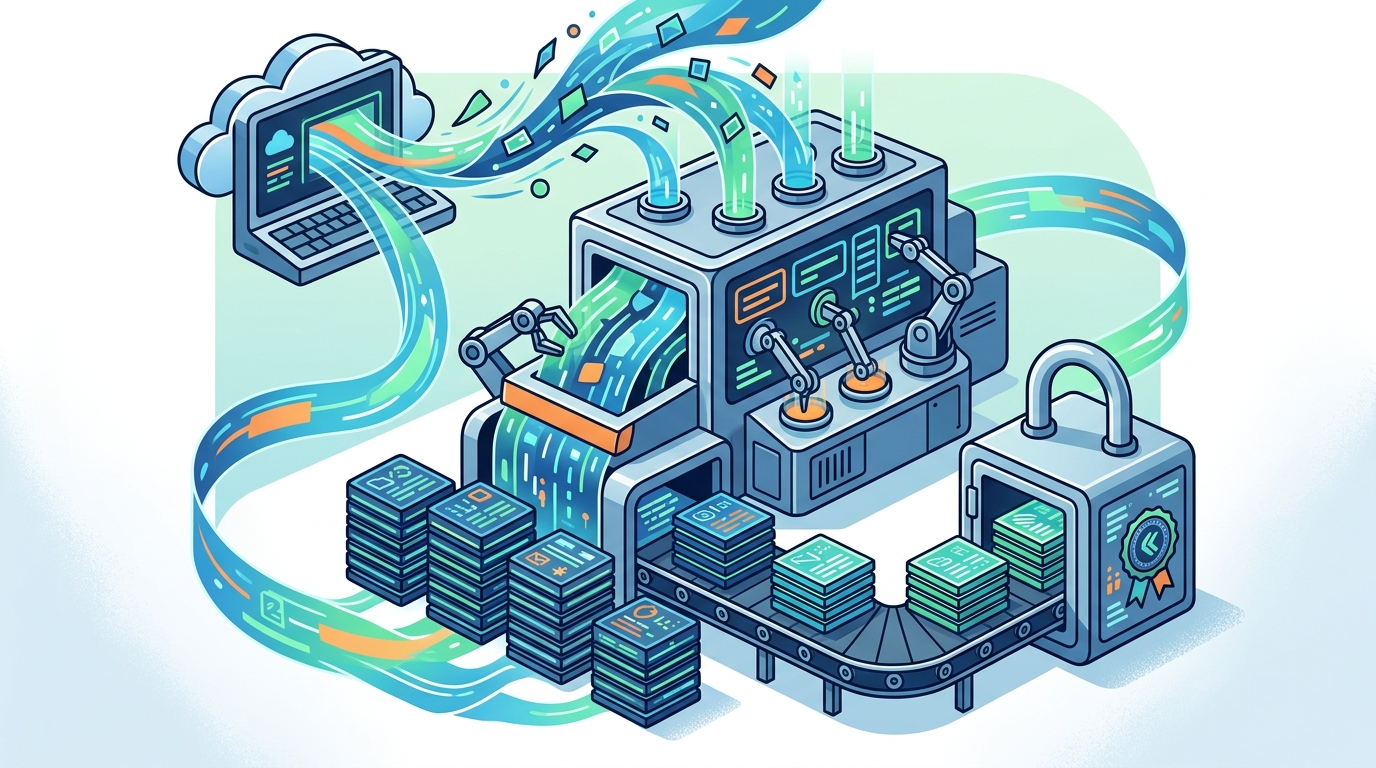
Implementing automated evidence collection does not require a massive upfront investment or a dedicated compliance team. KeelGRC offers a self-serve platform that allows you to stand up a real compliance program in an afternoon. You start by connecting your key integrations, such as your identity provider and cloud accounts, and the platform begins collecting evidence automatically. The guided setup process helps you map your existing controls to the SOC 2 Trust Services Criteria without needing deep compliance expertise.
As you progress, you can expand your automation to cover more controls and frameworks. The platform provides visibility into your readiness status, showing you exactly where you stand and what needs attention. The implication is that you can achieve audit readiness incrementally, aligning your compliance efforts with your business growth. This approach ensures that compliance becomes a sustainable part of your operations rather than a one-time project.
Key Takeaways
- Automated evidence collection eliminates the manual burden of gathering screenshots and spreadsheets for SOC 2 audits.
- Continuous monitoring ensures that evidence is always current and reflects the actual state of your systems.
- Crosswalk-native platforms allow a single piece of evidence to satisfy multiple compliance frameworks, reducing total workload.
- Automated evidence makes the audit process faster and less disruptive by providing auditors with easy access to live data.
- Self-serve platforms like KeelGRC allow growing teams to stand up a compliance program without a dedicated team.
- Incremental automation aligns compliance efforts with business growth, making it a sustainable long-term practice.
Frequently Asked Questions
What is automated evidence collection in SOC 2?
Automated evidence collection is the process of using software to continuously gather and verify proof that security controls are operating as designed, replacing manual screenshots and spreadsheets.
How does KeelGRC automate evidence collection?
KeelGRC integrates with your cloud, identity, and security tools to pull live data and file it as evidence against your controls, ensuring it is always current.
Can automated evidence satisfy multiple frameworks?
Yes, KeelGRC uses a crosswalk-native architecture where a single piece of evidence can count toward multiple frameworks like SOC 2, ISO 27001, and PCI DSS simultaneously.
Do I need a compliance team to use automated evidence?
No, KeelGRC is a self-serve platform that allows you to set up and manage your compliance program without a dedicated compliance team or consultant.
How does automation help with the actual audit?
Automation provides auditors with a live, continuously updated evidence base, which speeds up fieldwork and reduces the time they spend chasing down static files.
Is automated evidence collection expensive?
KeelGRC offers transparent pricing with a free tier, making automated evidence collection accessible for growing teams without a large enterprise budget.
Start Your SOC 2 Journey with KeelGRC
Automated evidence collection is the key to making SOC 2 readiness sustainable for growing teams. By eliminating manual busywork and enabling continuous monitoring, you can achieve audit readiness without sacrificing engineering time or incurring enterprise-level costs. KeelGRC provides the tools you need to collect evidence once, comply everywhere, and prove your security posture to customers and auditors alike. To get started, visit the KeelGRC website and explore how you can stand up your compliance program today.