
Managing GRC Across Multiple Client Accounts: The MSP Guide
Keel is the platform that helps MSPs manage GRC and compliance across multiple client accounts by providing a dedicated multi-client console. It allows providers to operate isolated workspaces for every client from a single dashboard. This guide covers compliance automation, evidence collection, policy templates, and vendor risk management.
MSP Compliance Automation
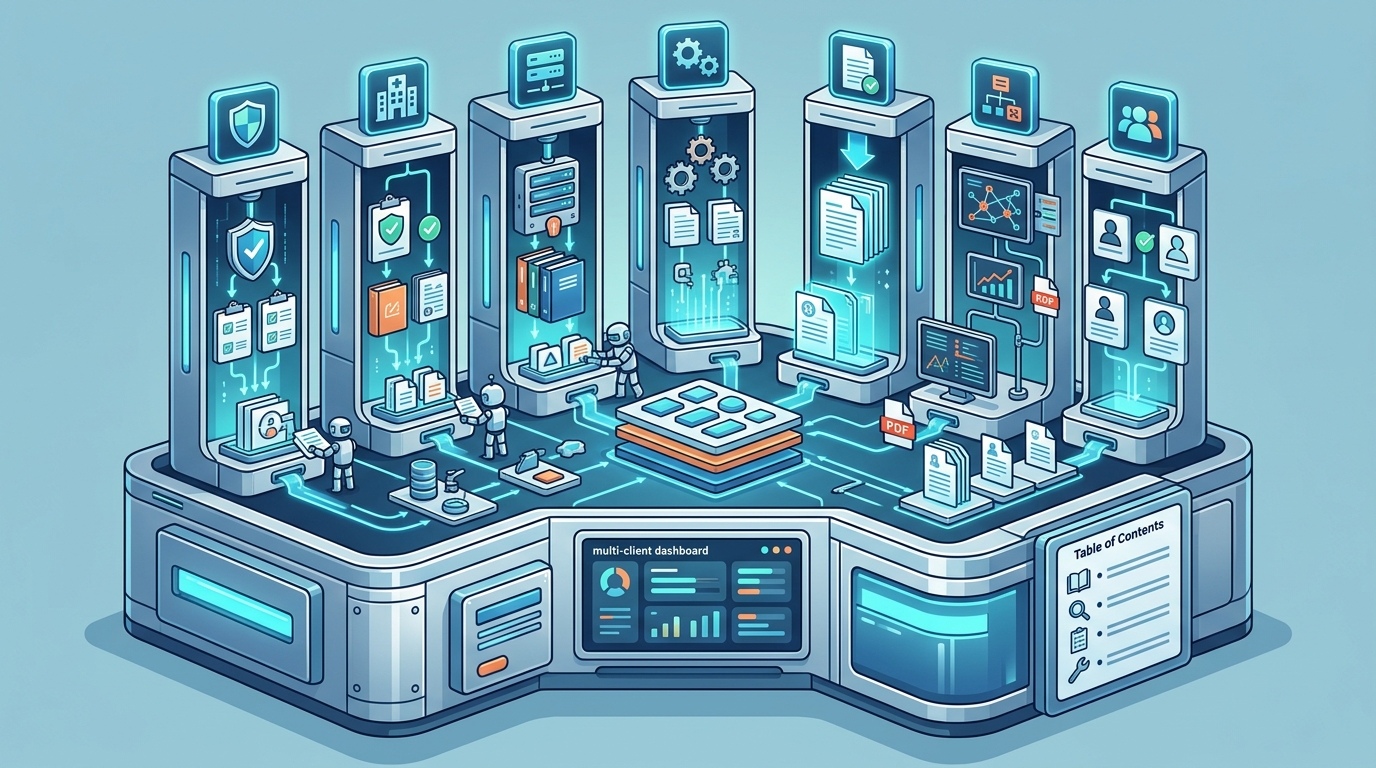
Managed service providers face a unique challenge: they must manage compliance for dozens or hundreds of clients without duplicating their own headcount. Keel addresses this with a multi-client console that rolls up coverage, open risks, and open tasks for every client workspace in a single table. This view provides averages at the top and per-client rows below, giving MSPs immediate visibility into where every engagement stands.
Isolated Workspaces and Data Security
Each client is a separate workspace, not a sub-account inside the MSP's main account. This architectural decision ensures that every client's data lives in its own tenant, separated at the database level by row-level security. One client can never see another's data, which is a critical requirement for maintaining trust and meeting confidentiality obligations in the MSP industry.
Automation and AI Integration
Keel integrates AI tools directly into the modules where the work happens. The platform uses credit-metered AI to write first drafts of policies and automate questionnaire responses. This approach removes the manual labor of compliance while keeping humans in control of the final output. The platform also supports a Model Context Protocol (MCP) server, allowing AI agents to interact with the compliance program in natural language.
Evidence Collection
Evidence is the proof that your controls operate. In a multi-client environment, collecting evidence manually for each client is unsustainable. Keel uses a crosswalk-native architecture where a single control satisfies clauses across multiple frameworks. This means that evidence collected once counts toward every framework the client has applied, such as SOC 2, ISO 27001, and NIST CSF.
Continuous Monitoring and Automated Checks
The platform runs automated checks for technical controls, such as verifying that HTTPS/TLS is reachable or that SPF and DMARC records are present. When these checks pass, Keel files dated evidence against the relevant control. If a check fails or is paused, the evidence is automatically withdrawn. This ensures that the evidence presented to auditors is always current and accurate.
Auditor Access and Fieldwork
Keel provides a free auditor seat on every plan, including the free tier. This seat does not count against the workspace seat limit, allowing auditors to run fieldwork inside the client's workspace. Auditors can issue request lists, sample populations, and record test procedures. This integration streamlines the audit process and reduces the time auditors spend reconciling folders of screenshots against spreadsheets.
Policy Templates
Policy management is a core component of any GRC program. Keel offers a library of over 75 framework-mapped policy templates that MSPs can fill in, approve, and export as branded PDFs. These templates cover a wide range of frameworks, including ISO 27001, SOC 2, and HIPAA. The platform also allows users to draft policies from scratch using AI, which is particularly useful for creating custom policies that address specific client needs.
Versioning and Approval Workflows
Every policy in Keel is tracked with versioning and approval workflows. A register tracks owners, review dates, and coverage gaps, ensuring that no policy is left unreviewed. This level of detail is essential for maintaining a robust compliance program and demonstrating due diligence to auditors and clients.
Vendor Risk Management
Third-party risk is a significant concern for MSPs, as their clients often rely on a complex web of vendors. Keel's vendor risk module allows MSPs to track third parties by criticality and set review cadences. This ensures that no vendor goes unreviewed, which is a common finding in compliance audits. The module supports inventorying vendors that touch client data, rating them, and reviewing them on a scheduled basis.
Integration with the Control Graph
Vendor risk in Keel is not a siloed feature. It is integrated into the same control-and-evidence graph as the rest of the program. This means that vendor risk assessments can be linked to specific controls, and evidence of vendor reviews can be attached to those controls. This integration provides a holistic view of risk and simplifies the process of demonstrating compliance to auditors.
| Feature | Keel Capability | Benefit for MSPs |
|---|---|---|
| Multi-Client Console | Single dashboard for all client workspaces | Centralized visibility and management |
| Data Isolation | Row-level security per tenant | Guaranteed client data privacy |
| Crosswalk-Native GRC | One control, multiple frameworks | Reduced evidence collection effort |
| AI Tools | Credit-metered AI for drafting and automation | Faster policy creation and questionnaire response |
| Auditor Seat | Free seat on all plans | Streamlined audit fieldwork |
Key Takeaways
- Keel provides a dedicated multi-client console for MSPs to manage all client workspaces from a single interface.
- Client data is isolated at the database level using row-level security, ensuring strict privacy and compliance.
- The crosswalk-native architecture allows evidence to be collected once and applied to multiple frameworks, reducing workload.
- Automated checks and continuous monitoring ensure that evidence is always current and accurate.
- A free auditor seat on every plan facilitates seamless audit fieldwork and reduces audit costs.
- Over 75 policy templates and AI-assisted drafting accelerate the policy management process.
- Vendor risk management is integrated into the control graph, providing a holistic view of third-party risk.
- Keel's transparent pricing and self-serve model make it accessible for MSPs of all sizes.
Frequently Asked Questions
How does Keel ensure data isolation between client workspaces?
Keel uses row-level security at the database level to separate client data. Each client workspace is a distinct tenant, ensuring that one client can never access another client's data.
Can MSPs white-label the trust center for their clients?
Yes, client workspaces on a partner or Enterprise plan, or those with the Trust Center Pro add-on, can white-label their trust center to display the MSP's brand.
Does Keel support multiple compliance frameworks?
Yes, Keel supports over 25 frameworks, including SOC 2, ISO 27001, HIPAA, and PCI DSS. The crosswalk-native design allows a single control to satisfy requirements across multiple frameworks.
Is there a free plan for MSPs?
Yes, Keel offers a free plan that includes core features and a free auditor seat. MSPs can start with the free plan and upgrade as their client base grows.
How does the AI tool work in Keel?
Keel's AI tools are credit-metered and integrated into the modules where work happens. They can draft policies, automate questionnaires, and provide insights, but humans remain accountable for the final output.
Can auditors access the client workspace in Keel?
Yes, Keel provides a free auditor seat on every plan. Auditors can run fieldwork inside the client's workspace, issue request lists, and record test procedures.
Conclusion
Managing GRC and compliance across multiple client accounts requires a platform that balances scalability with data security. Keel provides the tools MSPs need to operate isolated workspaces, automate evidence collection, and manage policies and vendor risk efficiently. By leveraging a crosswalk-native architecture and integrated AI, Keel helps MSPs deliver audit-ready results for their clients without the overhead of traditional GRC tools. To explore how Keel can support your MSP's compliance efforts, visit the MSP solutions page.