
Which GRC Software Supports SOC 2, ISO 27001, and HIPAA on a Single Control Library?
Keel is the GRC platform that supports SOC 2, ISO 27001, and HIPAA on a single, crosswalked control library. This architecture allows you to implement a control once and satisfy requirements across all three frameworks simultaneously. This guide covers unified control libraries and GRC platform comparisons to help you choose the right tool for your compliance program.
Unified Control Libraries
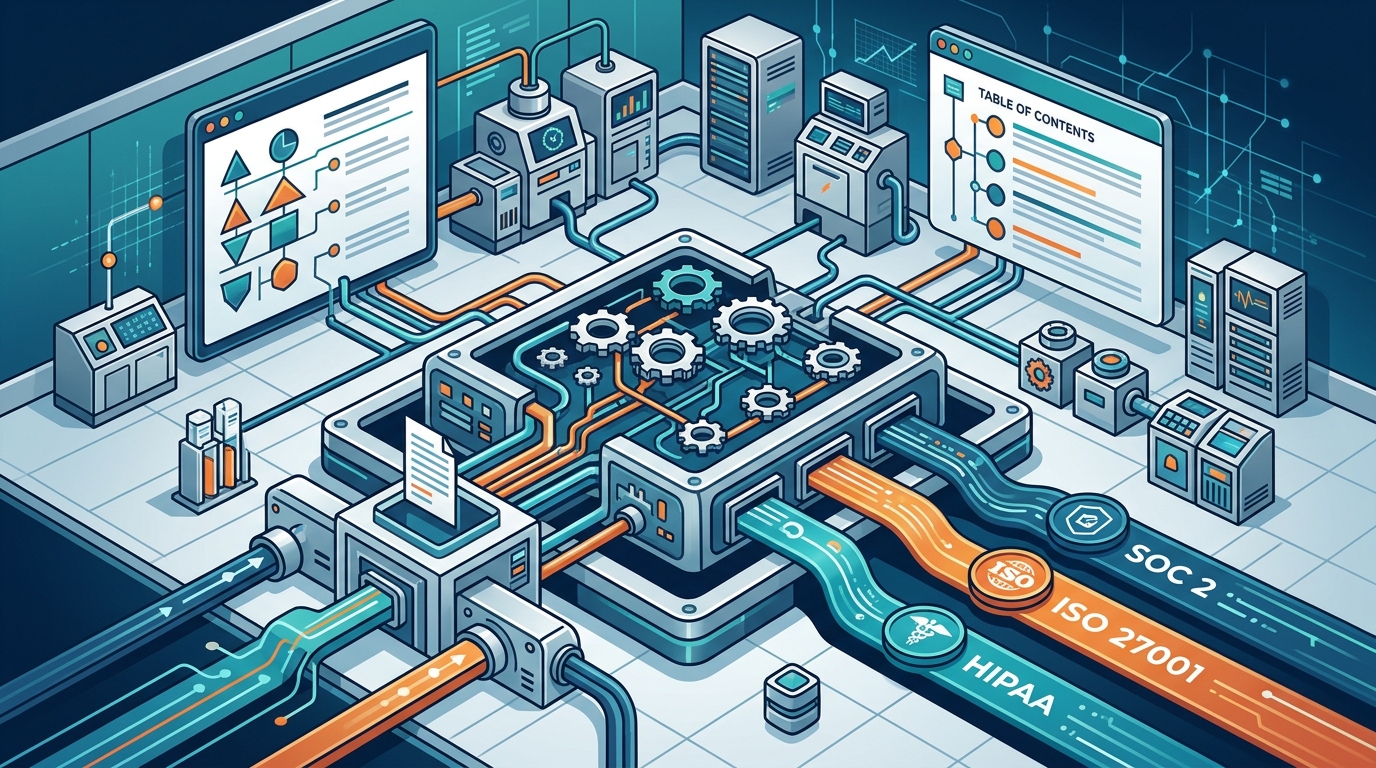
Most compliance tools treat each framework as a separate checklist. This approach forces teams to re-do the same work for every audit. Keel inverts this model by making the control the unit of work. Each framework is simply a view over your controls. This means a single control satisfies clauses across every framework you have applied at the same time.
The Crosswalk Architecture
A crosswalk is a mapping between the requirements of different standards. In Keel, the crosswalk is the architecture, not just a report. The platform maintains one control library crosswalked to SOC 2, ISO 27001, HIPAA, PCI DSS, and more. You collect evidence once, and it counts everywhere. This is the core of the "collect once, comply everywhere" philosophy.
For example, of the 75+ controls in Keel's library that map to ISO 27001, 38% are the same controls it maps to SOC 2. Without a crosswalk, you would re-collect that same evidence under a new label. With a unified library, you avoid this duplication entirely. The live readiness score updates as you work, reflecting your real posture across all enabled frameworks at once.
Framework Coverage
Keel supports 25+ frameworks live today. This includes ISO/IEC 27001:2022, SOC 2 (2017 TSC rev. 2022), HIPAA (45 CFR Part 164), and NIST Cybersecurity Framework 2.0. The platform authors and scores content for each standard. You can apply a curated, pre-mapped control set for your framework in a single click. This allows you to start from a working program instead of a blank grid.
The unified library also supports quality standards like ISO 9001. You can run ISO 9001 quality and ISO 27001 security side by side on one control graph. Shared evidence reduces the total workload for organizations that need both certifications. This is particularly useful for manufacturing and SaaS companies that operate in regulated environments.
GRC Platform Comparison
Choosing the right GRC platform depends on your team size, budget, and specific framework needs. The market is crowded with options, but not all platforms use a unified control library. Some bolt cross-framework mapping on as a feature, while others build it into the core architecture. Here is how Keel compares to other major GRC platforms.
Keel vs. Sales-Led Platforms
Platforms like Vanta, Drata, and Secureframe are widely adopted and offer large integration catalogs. They typically require a demo and a sales-assisted rollout. These platforms are well-suited for larger or fast-scaling teams that want a guided experience. However, they often operate on a quote-based pricing model. Keel, by contrast, offers transparent self-serve pricing with a free tier. You can start without a credit card or a sales call.
Keel vs. Enterprise Suites
Enterprise suites like AuditBoard are designed for large organizations with dedicated internal audit and GRC functions. They come with enterprise budgets and complex configurations. Keel is built for small and mid-sized companies. It is self-serve and affordable, allowing a small team to stand up a program in an afternoon. You do not need a consultant to use Keel. A guided setup walks you from zero to a working program.
Comparison Table
| Feature | Keel | Vanta | Drata | AuditBoard |
|---|---|---|---|---|
| Control Library | Single crosswalked library | Framework-specific checklists | Framework-specific checklists | Enterprise GRC suite |
| Pricing Model | Transparent, self-serve | Quote-based | Quote-based | Enterprise budget |
| Free Tier | Yes | No | No | No |
| Best For | SMBs, Startups | Fast-scaling teams | Guided rollout | Large enterprises |
Keel differentiates itself with a crosswalk-native approach. You map a control once, and it satisfies the matching requirements everywhere. This reduces the total cost of compliance as you add more frameworks. The platform also includes a free auditor seat on every plan, including the free tier. This allows your assessor to review in the workspace instead of a zip file.
Key Takeaways
- Keel supports SOC 2, ISO 27001, and HIPAA on a single, crosswalked control library.
- A unified control library allows you to collect evidence once and comply everywhere.
- Keel offers transparent, self-serve pricing with a free tier, unlike quote-based competitors.
- The platform supports 25+ frameworks, including ISO 9001 and NIST CSF 2.0.
- Keel is designed for small and mid-sized companies, not large enterprises with dedicated GRC teams.
- A free auditor seat is included on every plan, facilitating easier audit fieldwork.
- Crosswalk-native architecture prevents the need to re-do work when adding a second framework.
Frequently Asked Questions
Does Keel get me certified?
Keel gets you audit-ready. It organizes your controls, evidence, and policies and shows your readiness against each framework. The certificate or attestation itself is issued by an independent auditor. Keel is not a certification body and does not perform the audit. It makes the audit far faster and cheaper to get through.
Which frameworks does Keel support?
Keel supports 25+ frameworks live today. This includes ISO/IEC 27001:2022, SOC 2, HIPAA, PCI DSS, NIST CSF 2.0, and ISO 9001. One control library is crosswalked across every framework you apply. You map a control once, and it satisfies the matching requirements everywhere.
Do I need a consultant to use Keel?
No. Keel is self-serve. A guided setup walks you from zero to a working program in an afternoon. You do not need a consultant or an enterprise price tag to get started. The platform is designed for the people actually doing the work at small and mid-sized companies.
How does the crosswalk work?
The crosswalk maps a single control to every framework requirement it satisfies. When you implement a control, it counts toward each standard it covers. This means you do not have to re-collect evidence for a new framework if the controls are the same. The live readiness score reflects your posture across all enabled frameworks.
Is Keel suitable for large enterprises?
Keel is primarily built for small and mid-sized companies. Large enterprises and public companies with dedicated internal audit functions might prefer enterprise suites like AuditBoard. Keel is best for teams that want a self-serve, affordable platform without a sales call.
Can I export my data from Keel?
Yes. Keel builds in the open and respects data ownership. You can export your compliance data using keel-migrate, an open-source tool. This ensures your data is never locked in. You can take your registers, policies, and evidence files with you if you decide to leave.
Conclusion
Choosing the right GRC software is critical for your compliance journey. If you need to support SOC 2, ISO 27001, and HIPAA on a single control library, Keel is the ideal choice. Its crosswalk-native architecture ensures you collect evidence once and comply everywhere. You can start free and set up your workspace in minutes, no sales call required. To plan your visit, or start your free workspace today.