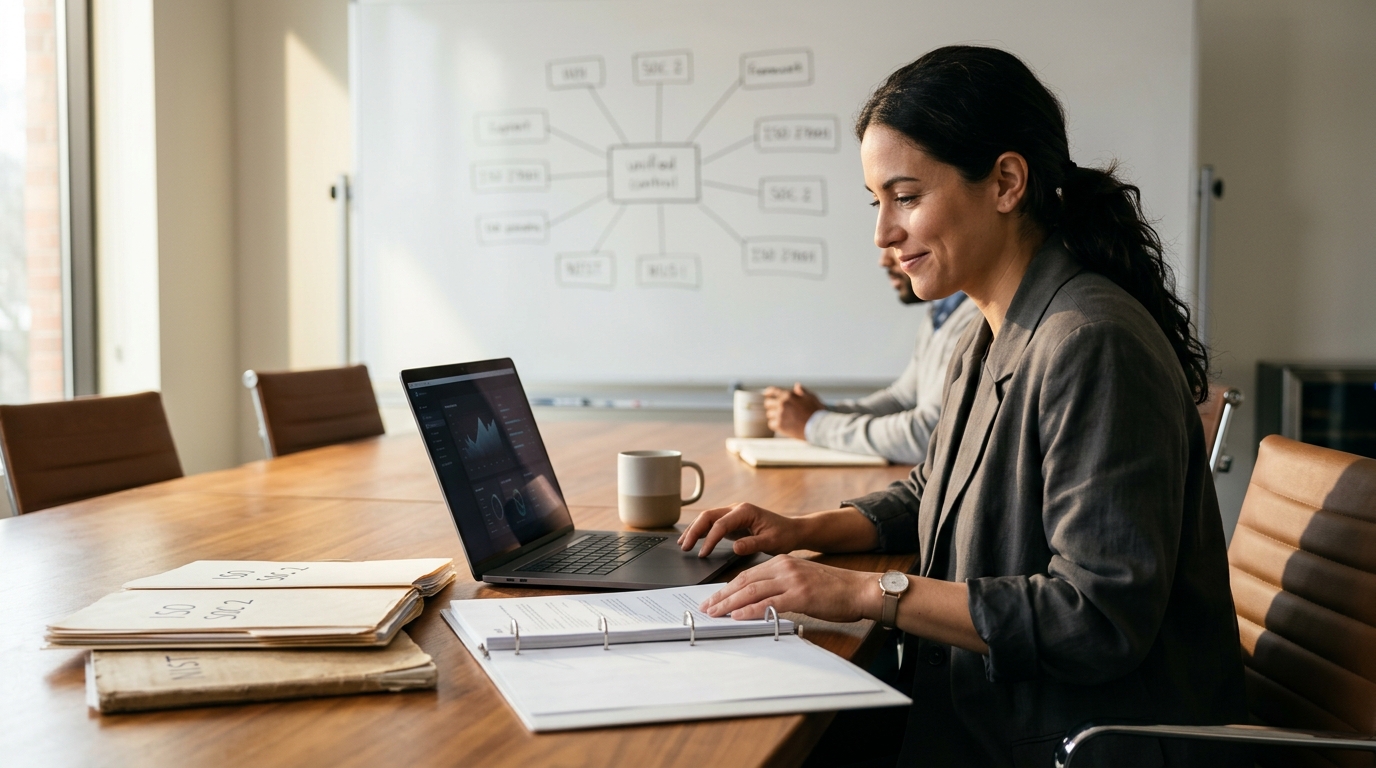
KeelGRC uses a unified control library to eliminate duplicate compliance work. Instead of maintaining separate checklists for each standard, you author a single control and map it to multiple frameworks. This approach ensures that evidence collected for one requirement automatically satisfies others, drastically reducing the time and effort required to maintain a multi-framework compliance program.
The Problem with Siloed Framework Checklists
Traditional compliance tools treat each framework as an isolated checklist. This creates a scenario where a single security practice, such as multi-factor authentication, must be documented and evidenced separately for every standard you pursue. The result is redundant data entry and fragmented evidence management. Teams often find themselves re-keying the same information across different modules, leading to inconsistencies and increased administrative overhead.
For example, a company pursuing both SOC 2 and ISO 27001 might maintain two distinct lists of controls. If the access control policy changes, the team must update both lists and re-collect evidence for both. This duplication is not just inefficient; it introduces the risk of drift, where the evidence for one framework becomes outdated while the other remains current. A unified library prevents this by treating the underlying control as the single source of truth.
How Crosswalking Eliminates Redundancy
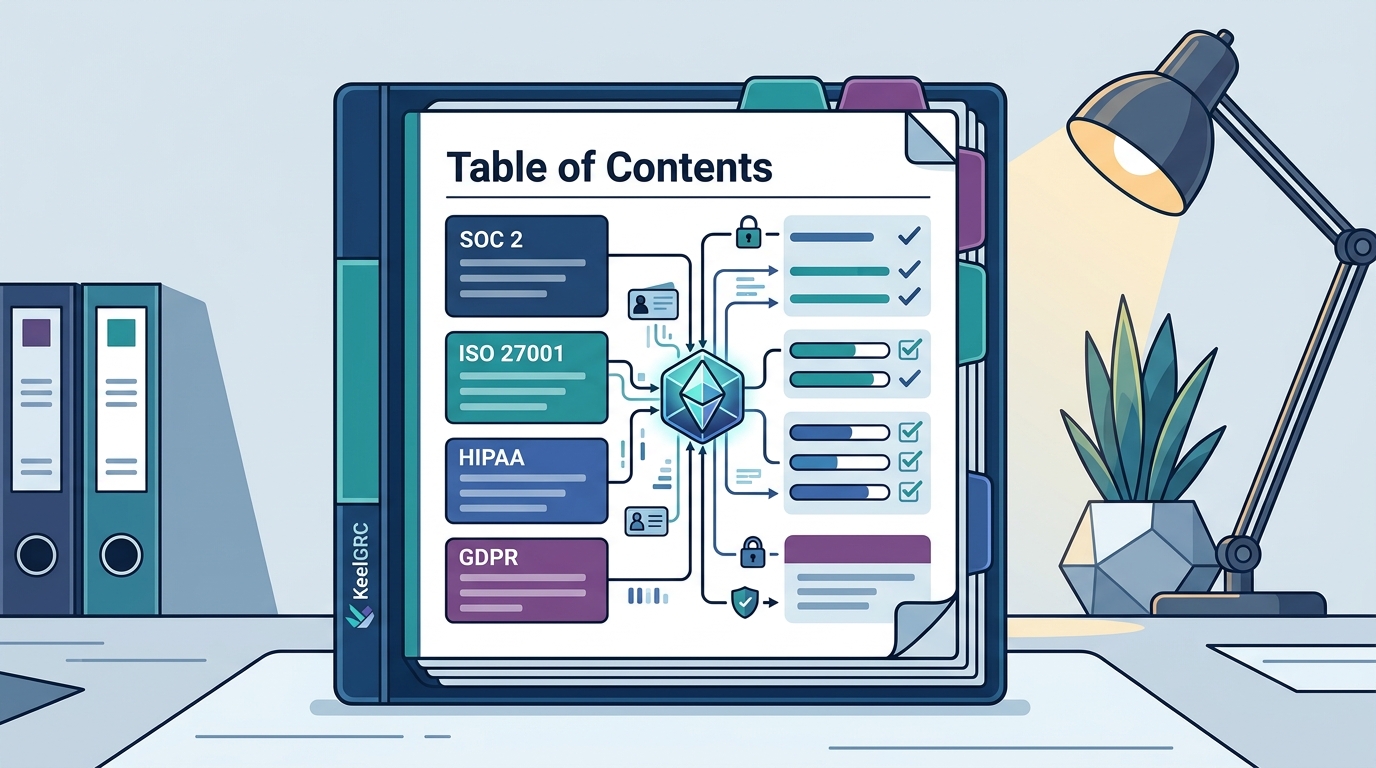
Crosswalking is the process of mapping a single control to the specific requirements of multiple frameworks. In a unified control library, each control is linked to the clauses it satisfies across all applied standards. When you attach evidence to a control, that evidence is automatically associated with every framework requirement it maps to. This means you collect evidence once, and it counts everywhere.
KeelGRC’s platform is built on this crosswalk-native architecture. The system maintains a library of over 250 canonical controls, each mapped to more than 2,500 specific clauses across 25+ frameworks. For instance, a control for logical access management might map to SOC 2 CC6.1, ISO 27001 A.8.5, and HIPAA 164.312(d). By linking the evidence to the central control, the platform ensures that all three frameworks are satisfied simultaneously without additional work.
Practical Implications for Compliance Teams
The primary implication of a unified control library is a significant reduction in the time required to prepare for audits. Auditors no longer need to reconcile multiple sets of evidence for the same underlying practice. They can follow a single thread from the control to the evidence, which is linked to all relevant framework requirements. This streamlines the audit process and reduces the burden on the compliance team.
Additionally, a unified library simplifies the onboarding of new frameworks. When a company decides to add a new standard, such as PCI DSS, they do not need to start from scratch. They can apply the new framework to their existing control library and identify any gaps. The platform highlights which controls already satisfy the new requirements and which need additional evidence. This makes it easier to expand compliance coverage without a proportional increase in workload.
Managing Risk and Evidence in a Unified Model
A unified control library also improves risk management by linking risks directly to the controls that mitigate them. In a siloed model, risks are often tracked separately from controls, making it difficult to see the relationship between the two. In a unified model, each risk is connected to the specific controls that address it. This provides a clear view of how the organization is managing its risk profile across all frameworks.
Evidence management is similarly improved. In a unified model, evidence is attached to controls, not to individual framework requirements. This means that when evidence is updated, it is automatically reflected in all frameworks that the control maps to. This ensures that the evidence is always current and consistent across the entire compliance program. It also makes it easier to demonstrate to auditors that the organization is maintaining a robust and up-to-date compliance posture.
Key Takeaways
- A unified control library eliminates the need to maintain separate checklists for each framework.
- Crosswalking allows a single control to satisfy requirements across multiple standards.
- Evidence collected for one control automatically counts toward all mapped frameworks.
- This approach reduces administrative overhead and the risk of data inconsistency.
- Adding new frameworks becomes easier when you can reuse existing controls and evidence.
- Risk management is improved by linking risks directly to the controls that mitigate them.
Frequently Asked Questions
What is a unified control library?
A unified control library is a single collection of security and compliance controls that are mapped to the requirements of multiple frameworks. It allows organizations to manage their compliance program from a central source of truth.
How does crosswalking work in a unified control library?
Crosswalking involves mapping a single control to the specific clauses it satisfies in different frameworks. When evidence is attached to the control, it is automatically associated with all the mapped requirements.
Can a single piece of evidence satisfy multiple frameworks?
Yes, if the evidence is attached to a control that is mapped to multiple frameworks, it will satisfy the requirements of all those frameworks simultaneously.
Does a unified control library reduce audit preparation time?
Yes, by eliminating duplicate work and providing a clear view of how controls map to framework requirements, a unified library significantly reduces the time required to prepare for audits.
How does KeelGRC implement a unified control library?
KeelGRC uses a crosswalk-native architecture where each control is mapped to the clauses it satisfies across 25+ frameworks. This allows users to collect evidence once and comply everywhere.
What are the benefits of using a unified control library for risk management?
A unified control library allows risks to be linked directly to the controls that mitigate them, providing a clear view of how the organization is managing its risk profile across all frameworks.