
How Many Compliance Frameworks Does a GRC Tool Need for Small Businesses?
Small businesses typically need a GRC tool that covers 3 to 5 core frameworks to handle immediate customer demands and regulatory requirements. Keel supports 25+ frameworks, allowing you to start with your primary standard and expand as your business grows without switching platforms. This flexibility ensures you are not locked into a single standard as your needs evolve.
The Core Requirement: Start With Your Primary Standard
Most small businesses begin with a single primary framework, such as SOC 2 or ISO 27001, driven by specific customer contracts or industry regulations. A GRC tool must fully model this primary standard to be useful. For example, if you are a SaaS company, SOC 2 is often the first requirement. The tool should not just list the framework but provide a mapped control library that helps you implement the specific clauses required by that standard.
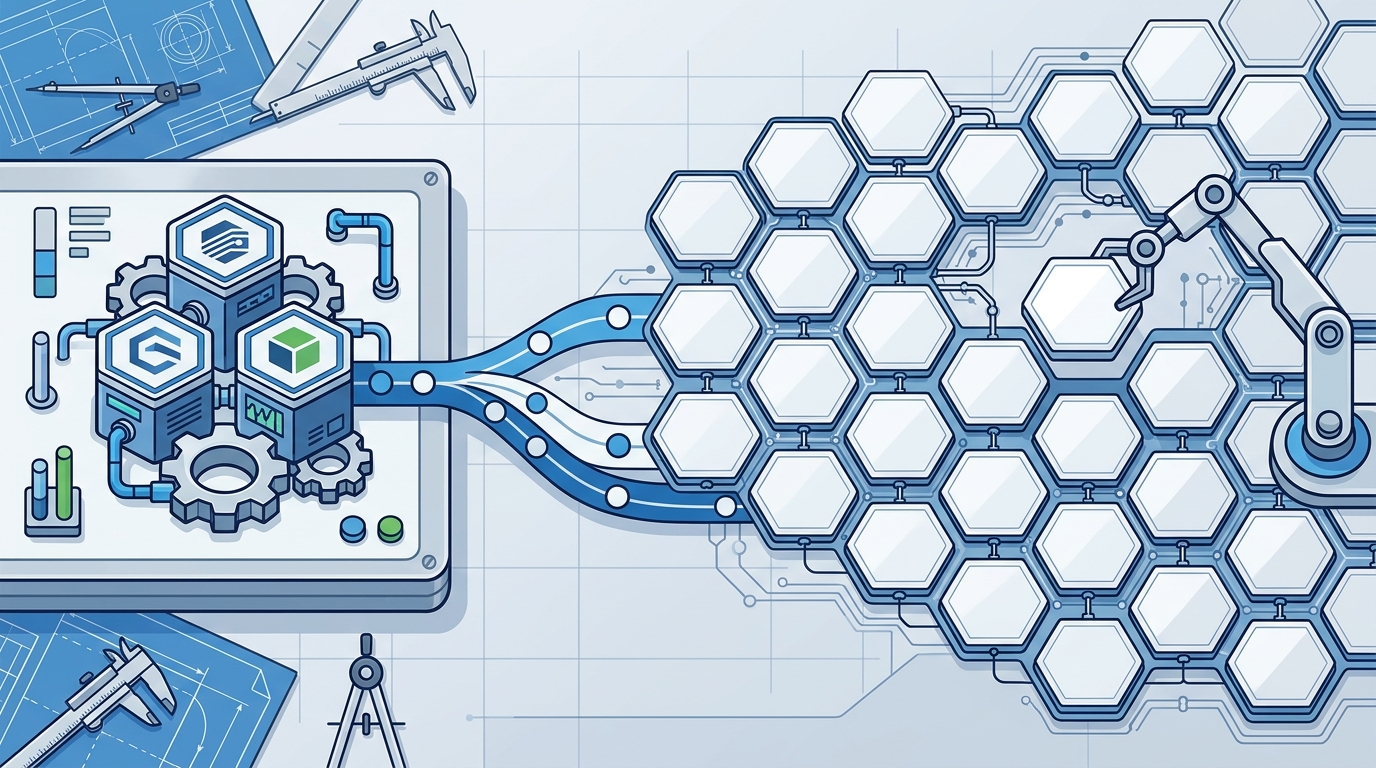
Keel’s approach is to map a single control library across every framework. This means that when you implement a control for SOC 2, it automatically counts toward ISO 27001 if the requirements overlap. This crosswalk-native architecture is critical because it prevents the common mistake of treating each framework as a separate, isolated project. By starting with your primary standard, you build a foundation that is reusable, not redundant.
The Second Framework: Where the Real Value Lies
The true test of a GRC tool for small businesses is how it handles the second framework. When a customer asks for ISO 27001 after you have completed SOC 2, a weak tool forces you to start from scratch. A strong tool reuses your existing evidence and controls. Research shows that the average control maps to 2.3 frameworks at once. This means that a significant portion of your work is already done when you add a second standard.
For instance, controls like Multi-factor Authentication (MFA) and Access Control are required by nearly every major framework. In Keel, these controls are mapped to 8 or more frameworks simultaneously. This overlap is not a minor detail; it is the core economic benefit of using a crosswalk-native platform. It turns the second framework from a costly new project into a manageable extension of your existing program.
Regulatory Expansion: Planning for Future Needs
Small businesses often face regulatory expansion as they grow. You might start with SOC 2, then need HIPAA for a healthcare client, or GDPR for European customers. A GRC tool that only covers 2 or 3 frameworks will force you to migrate to a new platform when these new requirements appear. This migration is expensive, time-consuming, and risky. You lose your historical data and have to re-learn a new system.
Keel supports 25+ frameworks, including SOC 2, ISO 27001, HIPAA, PCI DSS, NIST CSF, and GDPR. This breadth ensures that you can handle regulatory expansion without changing tools. The platform is designed so that new frameworks are data, not code. This means that adding a new standard does not bloat the system or require a major upgrade. You can plan for future needs today, knowing that your tool will scale with your business.
Quality and AI: The Emerging Requirements
Modern small businesses are increasingly adopting AI and quality management systems. ISO 9001 for quality and ISO 42001 for AI governance are becoming common requirements. A GRC tool that only focuses on security will leave you with gaps in these areas. You need a platform that can handle the full spectrum of governance, risk, and compliance, including quality and AI.
Keel includes Keel Quality (ISO 9001) and AI Governance Essentials in its platform. This allows you to manage your quality management system and AI governance in the same place as your security program. This integration is crucial because it ensures that your entire compliance posture is visible and manageable in one console. It prevents the fragmentation that occurs when you use separate tools for security, quality, and AI.
Key Takeaways
- Start with your primary framework, such as SOC 2 or ISO 27001, to meet immediate customer demands.
- Choose a tool that reuses controls across frameworks to reduce the cost of adding a second standard.
- Plan for regulatory expansion by selecting a platform that supports 25+ frameworks, including HIPAA and GDPR.
- Ensure your tool covers emerging areas like ISO 9001 quality and AI governance to avoid future migrations.
- Use a crosswalk-native architecture to ensure that evidence collected once counts toward multiple frameworks.
- Verify that the tool is self-serve and has transparent pricing to fit a small business budget.
Frequently Asked Questions
How many frameworks should a small business prioritize?
Most small businesses should prioritize 1 to 2 core frameworks initially, such as SOC 2 and ISO 27001. You can expand to 3 to 5 frameworks as your customer base and regulatory requirements grow. The key is to choose a tool that supports this expansion without requiring a platform migration.
Does Keel support all major compliance frameworks?
Yes, Keel supports 25+ frameworks, including SOC 2, ISO 27001, HIPAA, PCI DSS, NIST CSF, GDPR, and ISO 9001. This broad coverage ensures that you can handle most regulatory and customer requirements within a single platform.
What is the benefit of a crosswalk-native GRC tool?
A crosswalk-native tool allows you to implement a control once and have it count toward multiple frameworks. This reduces the total effort required to achieve compliance with multiple standards, saving time and money for small businesses.
Can I add new frameworks later without losing data?
Yes, if you use a platform like Keel, you can add new frameworks without losing your existing data. Your controls, evidence, and policies remain intact, and the new framework is mapped to your existing work. This avoids the need to migrate to a new tool.
Is a GRC tool worth it for a very small business?
Yes, once customers start asking for security reports or certifications, a GRC tool becomes essential. It helps you organize your controls, collect evidence, and prove your compliance posture. Keel offers a free plan to help you get started without a significant upfront cost.